Review an App for Pre-Deployment Security Risks
Review an application for common security weaknesses before deployment, including access-control, secrets, dependency, and error-handling issues.
Example outputs
Prompt template
- Format
- Text Parameterized
- Inputs
- application_materials (code, document, text) · Required
- Outputs
- security_review (text)
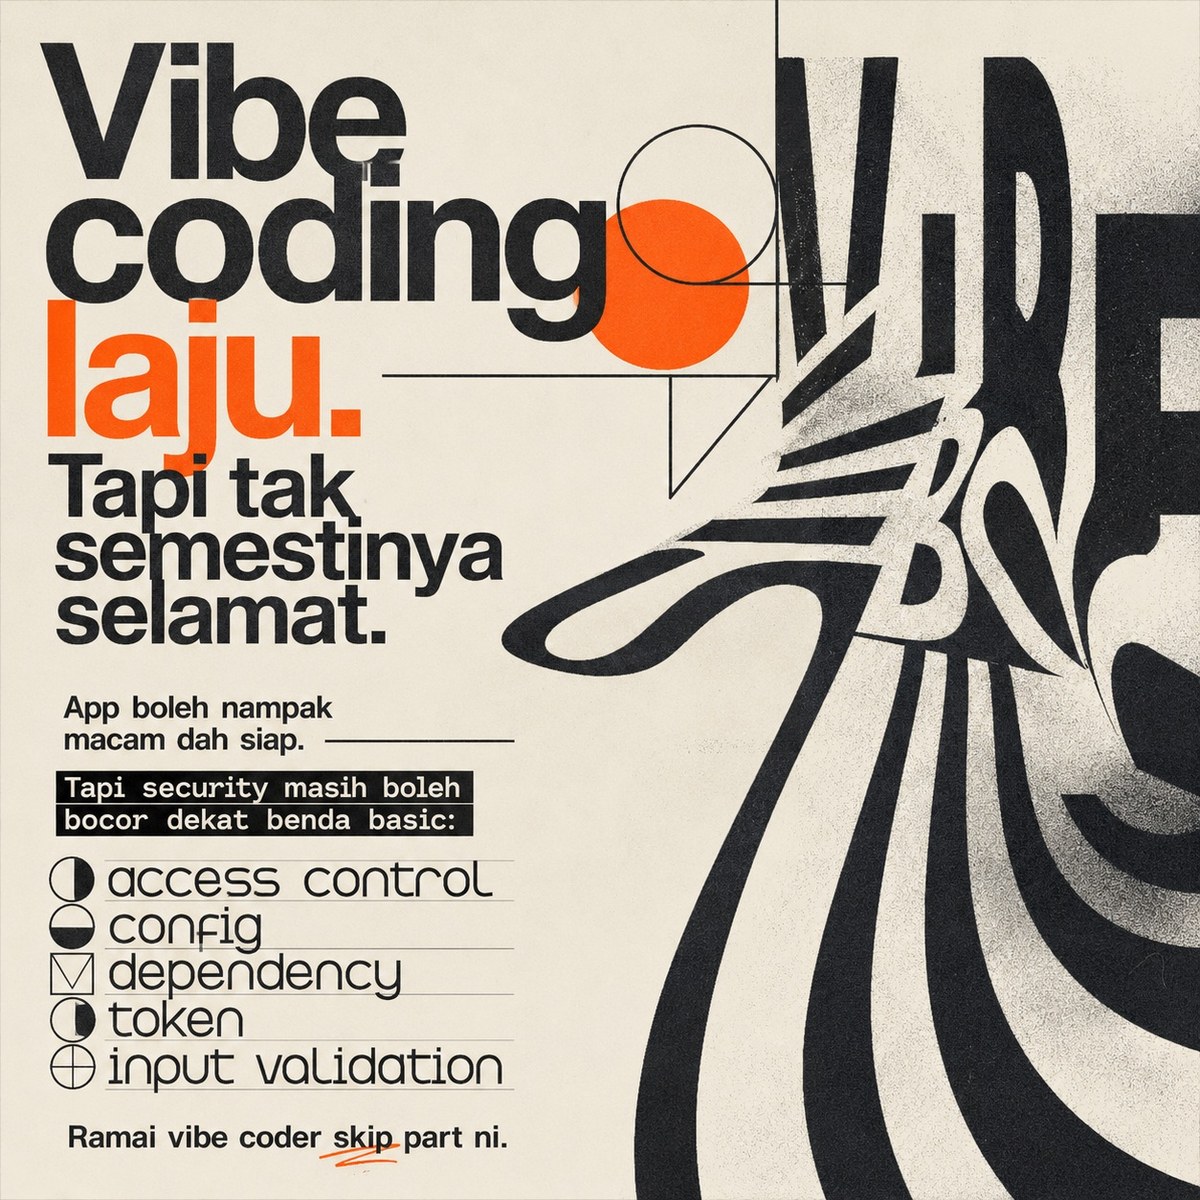
Review the application materials below for security risks before deployment. Treat AI-generated code as untrusted and assess it against the OWASP Top 10.

Specifically check:
- Whether one user can access another user's data.
- Whether admin routes are properly protected.
- Whether environment files or secrets are committed to Git.
- Whether API keys or other secrets are exposed in frontend code.
- Whether dependencies have known vulnerabilities.
- Whether error messages expose stack traces or other sensitive details.

Report each finding with its severity, the relevant file or code location when available, why it matters, and a practical remediation. Also identify checks you could not verify from the supplied materials. Do not assume the app is secure just because it runs.

Application materials:
${application-materials}
Replace the ${…} placeholders with your values
before using this prompt. See parameters
and defaults below
Parameters
Replace each placeholder with your own value, or use its default when one is provided
${application-materials}
application-materials
Required
What you'll create
A security assessment examines authorization, secret exposure, vulnerable dependencies and sensitive error details, reporting severity, locations and remediation.
Frequently asked questions
Does a running application prove it is secure?
No, the source explicitly warns against assuming security simply because the app runs.
Comments
Tried this prompt? Share what you made, compare results, or ask a question